ECHO · Write-ups · boroCTF 2026
boroCTF 2026: The Complete Write-Up
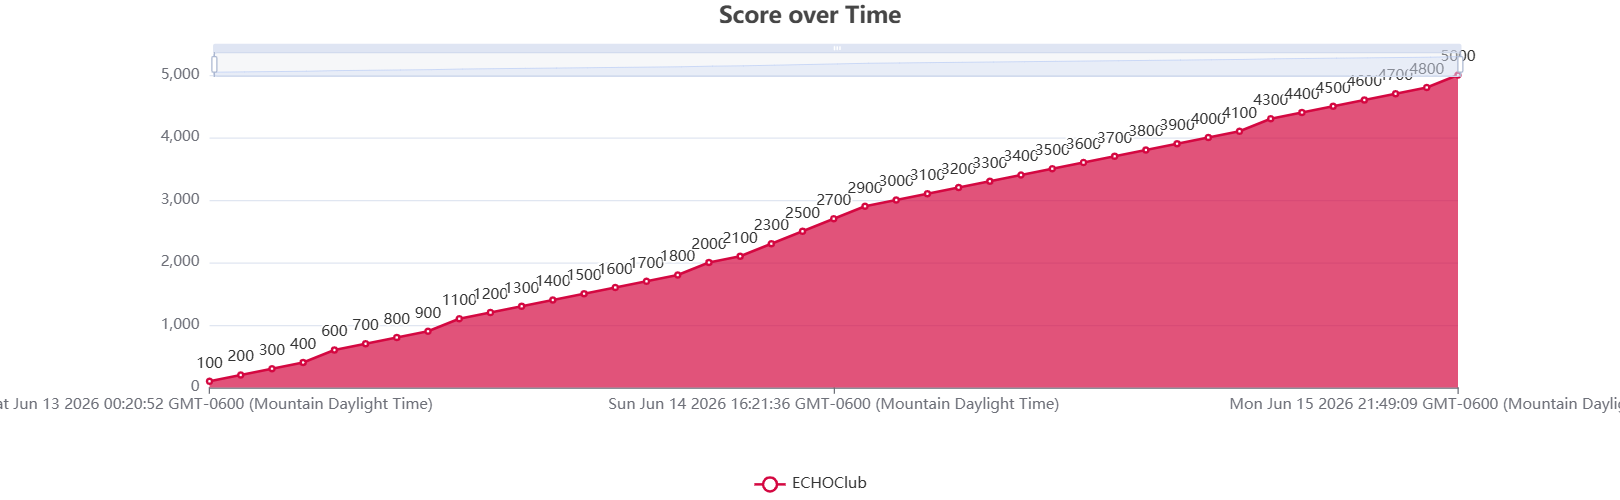
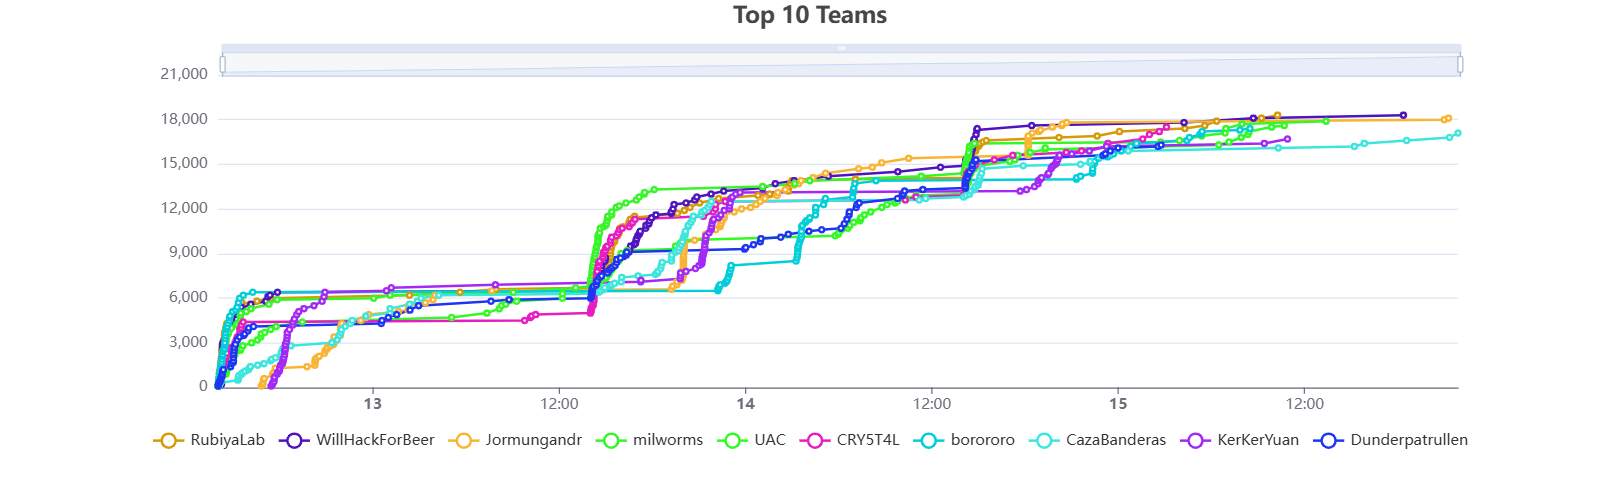
boroCTF 2026 ran 12–16 June, hosted at boroctf.com on CTFd v3.8.5. ECHOClub entered the open division as a solo competitor and finished with 41 solves for 5,000 points — 276th of 831 teams overall, 205th of 653 in the open division. This is every one of those solves, with the technique, the tooling and the flag. Nothing has been tidied into a success story; the entries that were guessed say so.
Provenance
Competed 13–15 June 2026 at boroCTF 2026, hosted by Freehold Borough and open to high-school and open-division competitors worldwide. One competitor, three days, six categories. This page is the club’s public setting of the master write-up report.
Disclaimer. This report documents challenge solutions completed on the boroCTF competition platform for educational purposes. All work was performed inside a controlled CTF environment against systems the competition provided for that purpose. ECHOClub is not responsible for the organisation or administration of the boroCTF platform.
On the flags. They are published deliberately. The competition is over, the scoreboard is frozen, and a write-up that withholds the answer teaches nobody how the answer was reached — which is the only reason this document exists.
Take it with you
PDF · the formatted competition report with the scoreboard figures — DOCX · the long-form source this page was set from
Section 1
Competition Results
41 solves · 5,000 points · 276th of 831 · solo
Forensics carried the run — 13 solves for 1,800 points, 36% of the total. OSINT followed with 11 solves, most of them links in a single fictional investigation chain (the Satoshi arc). All six available web challenges were solved. The competition used dynamic decay scoring, so an early solve was worth more than the same solve later, which is why the solve times below matter as much as the point values.
| Category | Solves | Points | % of total |
|---|---|---|---|
| Forensics | 13 | 1,800 pts | 36% |
| OSINT | 11 | 1,300 pts | 26% |
| Crypto | 7 | 700 pts | 14% |
| Web | 6 | 700 pts | 14% |
| Misc | 4 | 500 pts | 10% |
| Total | 41 | 5,000 pts | 100% |
Section 2
The Full Solve List
All 41 challenges in order of completion, as recorded on the official scoreboard
| Challenge | Category | Pts | Time | Flag |
|---|---|---|---|---|
| Boro Hero | OSINT | 100 | Jun 13, 12:20 AM | RedactedCTF{...} |
| Nature’s Takeover | OSINT | 100 | Jun 13, 12:23 AM | RedactedCTF{...} |
| The Squad | OSINT | 100 | Jun 13, 12:36 AM | RedactedCTF{...} |
| Satoshi Hunt | OSINT | 100 | Jun 13, 11:01 AM | RedactedCTF{...} |
| Satoshi’s Secret | OSINT | 200 | Jun 13, 11:54 AM | RedactedCTF{...} |
| Physical Access >> | OSINT | 100 | Jun 13, 2:33 PM | RedactedCTF{...} |
| Oops… | OSINT | 100 | Jun 13, 2:34 PM | RedactedCTF{...} |
| Fireman | OSINT | 100 | Jun 13, 2:57 PM | RedactedCTF{...} |
| Where there’s smoke, there’s fire. | OSINT | 200 | Jun 13, 4:47 PM | RedactedCTF{...} |
| Grep’n it | Forensics | 100 | Jun 13, 9:42 PM | RedactedCTF{...} |
| kitty kitty meow meow | Forensics | 100 | Jun 13, 10:03 PM | RedactedCTF{...} |
| Billie Eilish | Forensics | 100 | Jun 13, 10:30 PM | RedactedCTF{...} |
| The Shattered Needle | Forensics | 100 | Jun 13, 11:09 PM | RedactedCTF{...} |
| File Me to the Moon | Forensics | 100 | Jun 13, 11:10 PM | RedactedCTF{...} |
| Silent Sentinel | Forensics | 100 | Jun 13, 11:14 PM | RedactedCTF{...} |
| Satoshi: A Memory of The Past | Forensics | 100 | Jun 13, 11:20 PM | RedactedCTF{...} |
| A basic start | Crypto | 100 | Jun 14, 12:09 PM | RedactedCTF{...} |
| Retinal Burn | Forensics | 200 | Jun 14, 11:55 AM | RedactedCTF{...} |
| Looking through Windows | Forensics | 200 | Jun 14, 12:16 PM | RedactedCTF{...} |
| File-et Mignon | Forensics | 200 | Jun 14, 3:59 PM | RedactedCTF{...} |
| Chronos | Forensics | 200 | Jun 14, 4:21 PM | RedactedCTF{...} |
| Blackwall Protocol | Forensics | 200 | Jun 14, 4:54 PM | RedactedCTF{...} |
| Mark Zuckerburg | Forensics | 100 | Jun 14, 5:31 PM | RedactedCTF{...} |
| Boro Coin 1 | Crypto | 100 | Jun 14, 5:49 PM | RedactedCTF{...} |
| Et Tu, Brute | Crypto | 100 | Jun 14, 6:03 PM | RedactedCTF{...} |
| Not the Flag | Crypto | 100 | Jun 14, 6:05 PM | RedactedCTF{...} |
| Flipper’s Dilemma | Crypto | 100 | Jun 14, 6:07 PM | RedactedCTF{...} |
| So Many Layers | Crypto | 100 | Jun 14, 6:17 PM | RedactedCTF{...} |
| Flight | Crypto | 100 | Jun 14, 6:46 PM | RedactedCTF{...} |
| Hidden Meaning | OSINT | 100 | Jun 14, 7:09 PM | RedactedCTF{...} |
| Go Knicks! | OSINT | 100 | Jun 14, 7:11 PM | RedactedCTF{...} |
| Distortion | Misc | 100 | Jun 14, 7:22 PM | RedactedCTF{...} |
| Nature’s Delight | Misc | 100 | Jun 14, 7:22 PM | RedactedCTF{...} |
| Its a Simple Challenge Really | Misc | 100 | Jun 14, 7:32 PM | RedactedCTF{...} |
| 64 is life | Misc | 200 | Jun 14, 11:02 PM | RedactedCTF{...} |
| Beyond the Homepage | Web | 100 | Jun 15, 12:09 AM | RedactedCTF{...} |
| Cracking the Vault | Web | 100 | Jun 15, 12:15 AM | RedactedCTF{...} |
| boro-senpai 1 | Web | 100 | Jun 15, 12:22 AM | RedactedCTF{...} |
| dotdotslashflagtxt | Web | 100 | Jun 15, 12:55 AM | RedactedCTF{...} |
| Drone Dash | Web | 100 | Jun 15, 12:56 AM | RedactedCTF{...} |
| Jay W. Tee | Web | 200 | Jun 15, 9:49 PM | RedactedCTF{...} |
Section 3
OSINT
11 solves · 1,300 points · the Satoshi arc runs through most of them
OSINT · 100 pts · Jun 13, 12:20 AM
Boro Hero
The challenge asked for a famous Freehold High School alum who skipped his own graduation and went on to become a best-selling artist. Bruce Springsteen was born and raised in Freehold, NJ, and famously did not attend his graduation ceremony. Local knowledge closed this one faster than a search did.
Tools
Google search · local knowledge
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 12:23 AM
Nature’s Takeover
Identify a famous “nature reclaims it” location. Reverse image research landed on the SS Ayrfield, an abandoned WWII-era ship in Homebush Bay, Australia, now completely overgrown with mangroves — one of the most reproduced “nature takeover” images on the internet, which is exactly why it makes a fair OSINT target.
Tools
Google image search · reverse image lookup
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 12:36 AM
The Squad
Identify the squad name from the competition context. The CTFd profile lookup gave
KyteBytes as the identifier used in the challenge.
Tools
boroCTF platform · CTFd profile lookup
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 11:01 AM
Satoshi Hunt
The first link in the competition’s fictional Satoshi chain: track the
@SatoshiNakamuda account. Its profile and posts referenced Mount Fuji as
a location. Note the deliberate misspelling — Nakamuda, not Nakamoto —
which is the thread that ties four separate challenges together.
Tools
Twitter/X search · profile investigation
FlagRedactedCTF{...}
OSINT · 200 pts · Jun 13, 11:54 AM
Satoshi’s Secret
The account’s profile picture was styled as a VHS still, date-stamped FEB 2 ’59. That date is the Dyatlov Pass Incident — nine Soviet ski hikers who died under still-unexplained circumstances in the Ural Mountains. The prop was the clue; nothing in the text pointed at it.
Tools
Date research · VHS prop analysis · historical event lookup
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 2:33 PM
Physical Access >>
Given physical access to a locked Windows machine, name the bypass.
sethc.exe is Sticky Keys — replacing it with cmd.exe yields
a SYSTEM shell straight from the login screen with no credentials at all. The classic
accessibility backdoor, and the reason full-disk encryption is not optional on a laptop
that leaves the building.
Tools
Windows accessibility feature knowledge · sethc.exe /
utilman.exe research
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 2:34 PM
Oops…
Research the 2024 CrowdStrike global IT outage. It was caused by a faulty content
configuration update to CrowdStrike Falcon; the specific file responsible was
channel_file_291, which triggered a kernel panic and BSOD on millions of
Windows systems worldwide.
Tools
Outage post-mortems · incident reporting
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 13, 2:57 PM
Fireman
A Minecraft screenshot of a Wayne Manor build. Reverse image search plus Minecraft
community OSINT traced the build back to its creator, The4BDmaster. Yandex
outperformed Google Images on this one, which is a recurring pattern for
game-screenshot lookups.
Tools
Yandex reverse image search · Minecraft forums · Google Images
FlagRedactedCTF{...}
OSINT · 200 pts · Jun 13, 4:47 PM
Where there’s smoke, there’s fire.
The payoff of the Satoshi arc. Brainfuck code posted by the
@soulfullybinded account decoded to a message referencing
“Satoshi” and “Sid”; following the narrative thread across the
linked accounts resolved the fictional character’s full name.
Tools
dcode.fr (Brainfuck decoder) · Twitter/X OSINT · maigret · sherlock
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 14, 7:09 PM
Hidden Meaning
An acrostic. Taking the first letter of each word in the challenge text spelled the flag out directly — no tooling, and no tool would have found it, because every decoder assumes the ciphertext is the whole string rather than one letter per word.
Tools
Manual first-letter extraction
FlagRedactedCTF{...}
OSINT · 100 pts · Jun 14, 7:11 PM
Go Knicks!
Sports trivia — the challenge referenced NBA basketball and the Knicks franchise. Confirmed as the New York Knicks.
Tools
NBA knowledge · sports OSINT
FlagRedactedCTF{...}
Section 4
Forensics
13 solves · 1,800 points · the strongest category, and the hardest
Forensics · 100 pts · Jun 13, 9:42 PM
Grep’n it
A log file with the flag buried in its entries. Searching for the flag format extracted it directly. The flag text is the lesson.
grep 'boroCTF{' logfile.txt
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 10:03 PM
kitty kitty meow meow
Basic file forensics: an image examined for hidden data in metadata, EXIF fields and appended bytes past the image’s own end marker.
Tools
exiftool · strings · file ·
binwalk
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 10:30 PM
Billie Eilish
Audio steganography and metadata on a themed audio file — the flag was carried in the file’s tags rather than its waveform.
Tools
exiftool · mp3info · strings
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 11:09 PM
The Shattered Needle
Incident-response log forensics across a set of system logs. A recursive grep for the flag pattern located the entry. Worth stating plainly: this challenge and Grep’n it resolved to the same flag string — not a transcription error here, that is what the platform accepted for both.
grep -r 'boroCTF' ./
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 11:10 PM
File Me to the Moon
A file supplied without its extension. Magic-byte identification revealed the true format was a PowerPoint presentation, and the format name itself was the flag.
Tools
file · binwalk · magic-byte inspection
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 11:14 PM
Silent Sentinel
A network capture carrying an embedded JPEG transferred over HTTP/TCP. Carving the JPEG
out of the raw packet payloads and viewing it showed a Vanguard 1 satellite on
display at the Smithsonian National Air and Space Museum; strings on the
carved file confirmed it against the Smithsonian catalogue comment.
tshark -r space.pcap -Y 'tcp.payload' -T fields -e tcp.payload \
  | python3 # hex carve -> extracted.jpg

strings extracted.jpg | grep -i satellite
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 13, 11:20 PM
Satoshi: A Memory of The Past
The most interesting 100-pointer of the competition. An ELF binary
(satoshi_pulse_v2) printed a stream of CPU timing values — and nothing
else. The values were bimodal, and that was the encoding: a Flush+Reload cache
side-channel, simulated.
| Observed timing | Cache state | Decodes to |
|---|---|---|
| ~20,000 cycles | Cache miss | bit 1 |
| ~300–500 cycles | Cache hit | bit 0 |
Thresholding the stream at 10,000 cycles, then decoding the resulting bits in 8-bit MSB-first chunks as ASCII, produced the flag.
file satoshi_pulse_v2
strings satoshi_pulse_v2
./satoshi_pulse_v2

# threshold, then decode MSB-first
threshold = 10000
bits = [0 if n < threshold else 1 for n in timings]
flag = ''.join(chr(int(''.join(map(str, bits[i:i+8])), 2))
               for i in range(0, len(bits), 8))
FlagRedactedCTF{...}
Forensics · 200 pts · Jun 14, 11:55 AM
Retinal Burn
Image steganography where the payload lived in visual artefacts and colour-channel encoding rather than in metadata. Channel-by-channel inspection surfaced it.
Tools
stegsolve · zsteg · ImageMagick ·
colour channel analysis
FlagRedactedCTF{...}
Forensics · 200 pts · Jun 14, 12:16 PM
Looking through Windows
NTFS disk-image forensics with deleted-file recovery. A VHD was mounted to a loop device
at the correct byte offset. The filesystem looked empty — and
ntfsundelete found a deleted ZIP archive at inode 39 anyway. The archive was
password-protected; a dictionary attack against rockyou.txt recovered
forget9293628 1 and the extraction gave up the flag.
losetup -o 1048576 /dev/loop0 disk.vhd
mount -t ntfs-3g /dev/loop0 /mnt/vhd
ntfsundelete /dev/loop0 -u -i 39 -d recovered/
fcrackzip -u -D -p /usr/share/wordlists/rockyou.txt recovered.zip
FlagRedactedCTF{...}
Forensics · 200 pts · Jun 14, 3:59 PM
File-et Mignon
A file that reported itself as 10 TB and contained 32 KB of actual
data. It was a sparse file, and every standard tool either refused it or tried to read ten
terabytes of holes. The correct instrument is os.lseek() with
SEEK_DATA and SEEK_HOLE, which walks straight from one real
region to the next: eight of them, spaced at exact 1 TB intervals, 4,096 bytes each.
Reading those eight chunks in order assembled the flag.
du -sh file          # ~32K actual, not 10T

import os
fd  = os.open('file', os.O_RDONLY)
pos = os.lseek(fd, 0, os.SEEK_DATA)
# loop: read 4096 at pos, then SEEK_HOLE -> SEEK_DATA for the next region
FlagRedactedCTF{...}
Forensics · 200 pts · Jun 14, 4:21 PM
Chronos
A PCAP whose packets carried nothing useful — the data was in when they arrived, not what they said. Inter-arrival delays were bimodal at roughly 0.25 s and 0.75 s; thresholding at 0.5 s gave a bitstream. The starting bit alignment was unknown, so all eight offsets were brute-forced and the one producing printable ASCII was the answer.
tshark -r chronos.pcap -T fields -e frame.time_delta

bits = [0 if d < 0.5 else 1 for d in deltas]
for off in range(8):                      # brute-force alignment
    out = ''.join(chr(int(''.join(map(str, bits[i:i+8])), 2))
                  for i in range(off, len(bits) - 8, 8))
FlagRedactedCTF{...}
Forensics · 200 pts · Jun 14, 4:54 PM
Blackwall Protocol
The same trick as Chronos, disguised twice over. The file carried a
.bd extension and was actually a PCAP — file gave that away
immediately. The timing scale was three orders of magnitude tighter: ~150 µs for
a zero, ~650 µs for a one, threshold at 400 µs. Bit alignment offset
7 was the correct starting position.
file blackwall.bd    # -> pcap, not whatever .bd implies
tshark -r blackwall.bd -T fields -e frame.time_delta

bits = [0 if d < 400e-6 else 1 for d in deltas]   # offset 7, MSB-first
FlagRedactedCTF{...}
Forensics · 100 pts · Jun 14, 5:31 PM
Mark Zuckerburg
An image whose EXIF and embedded comment fields held the flag. The challenge name is the hint — look past what the picture shows to what the file records about itself.
exiftool image.jpg
strings image.jpg | grep boroCTF
FlagRedactedCTF{...}
Section 5
Cryptography
7 solves · 700 points · encoding ladders, mostly
Crypto · 100 pts · Jun 14, 12:09 PM
A basic start
Base64, straight. The most fundamental encoding scheme in the category, decoding directly to the flag.
echo 'base64string' | base64 -d
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 6:03 PM
Et Tu, Brute
“Et Tu, Brute” is Shakespeare’s Julius Caesar — the challenge name names the cipher. Brute-forcing all 25 ROT shifts revealed the plaintext.
Tools
CyberChef ROT13 / Caesar Brute Force
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 6:05 PM
Not the Flag
Misdirection. The name suggests a decoy, but the real flag was embedded in the encoded data all along; applying the standard decode chain surfaced it.
Tools
CyberChef Magic · strings · base64 / hex decode
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 6:07 PM
Flipper’s Dilemma
Bit-level manipulation — flipping specific bits, or reversing bit order, to recover the message.
Tools
Python bit manipulation · CyberChef Bit Manipulation
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 6:17 PM
So Many Layers
A triple-layer encoding: binary to hex, hex to a base64 string, base64 to the flag. Peel one layer, get another encoding rather than an answer — the challenge name is the instruction.
binary -> chr(int(b, 2)) -> bytes.fromhex() -> base64.b64decode()
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 6:46 PM
Flight
An aviation-themed encoding challenge — data presented in a flight-adjacent format (NATO alphabet, Morse, or coordinates) and decoded back to text.
Tools
CyberChef · Morse decoder · dcode.fr
FlagRedactedCTF{...}
Crypto · 100 pts · Jun 14, 5:49 PM
Boro Coin 1
A fictional blockchain (Boro Coin) analysed for data hidden in transaction metadata,
OP_RETURN fields and block comments — the places a real chain lets you
write arbitrary bytes.
Tools
Blockchain explorer · transaction metadata analysis · hex decode
FlagRedactedCTF{...}
Section 6
Web Exploitation
6 solves · 700 points · all six available challenges, cleared
Web · 100 pts · Jun 15, 12:09 AM
Beyond the Homepage
robots.txt enumeration. The file exists to tell crawlers what not to index,
which makes it the first place an attacker looks — it is a list of the paths someone
wanted hidden.
curl http://target/robots.txt
FlagRedactedCTF{...}
Web · 100 pts · Jun 15, 12:15 AM
Cracking the Vault
A login portal that accepted common default credentials. Default and weak credentials remain one of the highest-yield findings in real assessments, which is why they are worth 100 points and thirty seconds.
Tools
Burp Suite · manual credential testing · default credential lists
FlagRedactedCTF{...}
Web · 100 pts · Jun 15, 12:22 AM
boro-senpai 1
The flag sat in the page’s own HTML — an HTML comment, hidden form field or meta tag. View-source found it.
curl http://target | grep boroCTF
FlagRedactedCTF{...}
Web · 100 pts · Jun 15, 12:55 AM
dotdotslashflagtxt
The challenge name is the exploit written out loud: ../../flag.txt. A file
path parameter took traversal sequences without sanitising them, reading a file from
outside the web root.
curl 'http://target/download?file=../../flag.txt'
# URL-encoded, when the naive form is filtered: %2e%2e%2f
FlagRedactedCTF{...}
Web · 100 pts · Jun 15, 12:56 AM
Drone Dash
A drone-delivery themed web app hiding an API endpoint. Enumerating endpoints and manipulating request parameters exposed the flag.
Tools
Browser dev tools · curl · Burp Suite · endpoint
enumeration
FlagRedactedCTF{...}
Web · 200 pts · Jun 15, 9:49 PM
Jay W. Tee
Say the name aloud: JWT. The site accepted any login credentials and returned a
signed JSON Web Token carrying role: guest. The alg:none
vulnerability — where a server honours the token’s own claim that it needs no
signature — allowed a forged token with role: admin and an empty
signature to be accepted outright.
header  {"alg":"none","typ":"JWT"}
payload {"username":"admin","role":"admin"}
signature // empty - the token ends on a trailing dot

// base64url-encode both parts, paste over the cookie in dev tools
The fix is one rule, and it is the reason this challenge is worth teaching: the server
must enforce the algorithm it expects and must never read alg out of the
token to decide how to verify that same token.
FlagRedactedCTF{...}
Section 7
Miscellaneous
4 solves · 500 points
Misc · 100 pts · Jun 14, 7:22 PM
Distortion
A deliberately distorted file. Undistortion techniques — spectral analysis, image dewarping, frequency-domain inspection — recovered the hidden content.
Tools
Audacity (spectrogram view) · stegsolve · ImageMagick
FlagRedactedCTF{...}
Misc · 100 pts · Jun 14, 7:22 PM
Nature’s Delight
A barcode from a Poland Spring water bottle. Scanning it, or looking the number up, identified the product — and the product name was the flag.
Tools
Barcode scanner · Google Lens · barcode lookup
FlagRedactedCTF{...}
Misc · 100 pts · Jun 14, 7:32 PM
Its a Simple Challenge Really
The name is honest: a basic ROT, base64 or hex decode that rewarded trying the simplest tool first rather than assuming a 100-point challenge must be hiding something.
Tools
CyberChef · base64 -d · xxd · ROT13
FlagRedactedCTF{...}
Misc · 200 pts · Jun 14, 11:02 PM
64 is life
The filenames were the puzzle. Each file carried a base64-encoded name; decoding the names gave an ordering, and reassembling the file contents in that order produced one complete base64 string which decoded to the flag.
for f in *; do echo "$(echo $f | base64 -d)"; done | sort
cat reassembled | base64 -d
FlagRedactedCTF{...}
Section 8
Key Lessons
What outlived the flags
Manual beats automation for non-standard encodings
A Wingdings challenge used Undertale’s variant of the font, whose Unicode codepoints differ slightly from the standard Microsoft mapping. Every automated decoder failed on it. Manual lookup against a Wingdings reference chart decoded three characters the machines got wrong. When a decoder returns almost right, suspect the mapping before you suspect the ciphertext.
Timing side-channels hide in the metadata, not the payload
Three separate challenges — Chronos, Blackwall Protocol and Satoshi: A Memory of The Past — encoded their data in timing rather than content: packet inter-arrival delays in two cases, CPU cache access latency in the third. The method is the same each time: pull the timing series, find the bimodal split, threshold it into bits, then brute-force the bit alignment offset 0–7 because you never know where the stream starts. A capture whose payloads are empty is not a dead capture.
Sparse files need SEEK_DATA, not a bigger disk
File-et Mignon reported 10 TB and held 32 KB. Standard tools choke on
that. os.lseek() with SEEK_DATA and SEEK_HOLE maps
the real regions directly — the right instrument turns an impossible read into eight
4 KB reads.
An empty disk image is not an empty disk
Looking through Windows mounted clean and showed nothing. ntfsundelete
against the loop device recovered a deleted ZIP at inode 39 that a normal mount will never
show you. Deleted is a flag in a table, not an erasure — which is exactly why
“we deleted the files” is not a remediation.
Challenge names are always hints
boroCTF put the attack vector directly in the title over and over: Jay W. Tee (JWT), dotdotslashflagtxt (path traversal), Et Tu, Brute (Caesar cipher), File Me to the Moon (file identification), 64 is life (base64). Reading the name carefully before touching the files saved more time than any tool did.
JWT alg:none is still deployed in the wild
The alg:none hole eliminates signature verification entirely, and it is not
a museum piece — it is still shipping. Servers must enforce the expected algorithm
server-side and must never trust the alg field carried by the token they are
about to verify.
boroCTF 2026 — ECHOClub competition write-up report
41 solves · 5,000 points · 276th of 831 overall, 205th of 653 open division · solo · educational use only. Competed. Solved. Learned. Stay curious.